A live risk register for every supplier
Tiering decides the checks, inherent risk is worked out for you, residual risk is rated by area and re-assessments fall due on their own. Every result is saved as evidence for your auditors.
Tiering that sets the checks
Five questions and the annual value recommend a tier from T1 Strategic to T4 Transactional. The tier decides the due diligence, who signs off go-live and how often you review.
Inherent risk, scored for you
From the tier, the data the supplier holds, access to your systems or sites and its use of AI. Nothing to type in.
Residual risk by area
Security, financial, data protection and geographic or concentration risk, each rated after your checks and controls. The worst sets the overall rating.
Re-assessments that run themselves
Due dates set by tier, shortened for high risk. Starting one sends the right tasks to Legal, Security, Finance, Privacy and Procurement.
How risk is rated
Tier and risk are kept separate. Tier says how closely you manage a supplier; risk says what could go wrong. A small supplier can still be high risk.
Inherent risk: before any checks
Inherent risk is worked out for you from five factors. Nothing needs typing in.
| Factor | Adds |
|---|---|
| Tier | T4: 0 points · T3: 1 · T2: 2 · T1: 3 |
| Data the supplier holds | None: 0 points · Internal or operational: 1 · Customer data: 2 |
| Access to your systems or sites | 1 point |
| Uses AI with your data | 1 point |
| That AI makes or supports decisions about people | 1 point |
Residual risk: after your checks and controls
Your team rates security, financial, data protection and geographic or concentration risk as Low, Medium or High, using the security questionnaire, privacy assessment, contract terms and financial checks. Any High makes the supplier High; otherwise any Medium makes it Medium. This is the figure to act on, and a named manager can record accepting it.
Where each risk area is covered
The six areas most TPRM frameworks look at, and what SupplierVault does about each. See every check in full.
| Risk area | What SupplierVault checks | Rated as residual risk? |
|---|---|---|
| Information security | Third-party risk request, security questionnaire (SOC 2, ISO 27001, MFA, encryption, pen testing, Cyber Essentials, incident reporting), certificates tracked to expiry, ISO 27001 supplier controls checklist. | Yes |
| Data protection | Internal privacy assessment, hosting location, international transfer mechanism, sub-processors, DPIA and the DPA. | Yes |
| Financial | Companies House look-up and weekly monitoring (including owners added or removed), financial health indicators, financial viability check, and your share of the supplier's turnover. | Yes |
| Concentration and geographic | Country risk for where the supplier is based and where its goods come from (corruption, FATF lists, UK sanctions, forced and child labour in goods); fourth parties the service depends on; concentration-risk review for T1, re-reviewed at each re-assessment; where data is held. | Yes |
| Operational and continuity | Business-critical flag, business continuity and recovery plans, SLAs and service credits, named owners, exit and continuity plan, and FCA material outsourcing records. | Through criticality, tier and the continuity review |
| Compliance and conduct | UK, US, UN and EU sanctions screening of the supplier, its directors and its owners, with monthly re-screens; an AI-assisted adverse media search; modern slavery including forced and prison labour; anti-bribery and fraud; code of conduct; AI use. | Through the sanctions result and form approvals, which drive the register's traffic lights |
Re-assessments
Each tier has a cycle you can change. A supplier with high inherent risk is re-assessed at least every 6 months, whatever its tier.
| Tier | Due diligence | Go-live approval | Risk re-assessment |
|---|---|---|---|
| T1 Strategic partner | Enhanced | Executive or senior leader | Every 3 months |
| T2 Key supplier | Standard-plus | Senior manager | Every 6 months |
| T3 Approved supplier | Standard | Department manager | Every 12 months |
| T4 Transactional | Simplified | Supplier manager or Procurement | When something changes |
Starting a re-assessment creates: sanctions and entity re-screen (Legal), refresh of the security questionnaire and evidence (Security), financial health check (Finance), privacy review (Privacy), code of conduct re-attestation (Procurement), concentration and continuity review (Procurement), and risk sign-off with the residual rating (Security).
The TPRM register
One row per supplier, with tier, inherent and residual risk, data and access, sanctions, modern slavery and form status, certificates and the next review. Ordered most urgent first.
- Red, act now: a possible sanctions match, a live supplier overdue, never assessed or not screened, or an expired certificate.
- Amber, attention: a re-assessment due within 60 days, a certificate expiring within 45 days, high residual risk, or security, privacy, code of conduct or AI forms not yet approved.
- Green, in date: assessed, screened and in date.
- Edit in place to update ratings, access, sanctions results and certificate dates without opening each record. Every change is logged.
- Export the register as a spreadsheet, or run the Risk register and Executive supplier reports.
One report for auditors, boards and customers
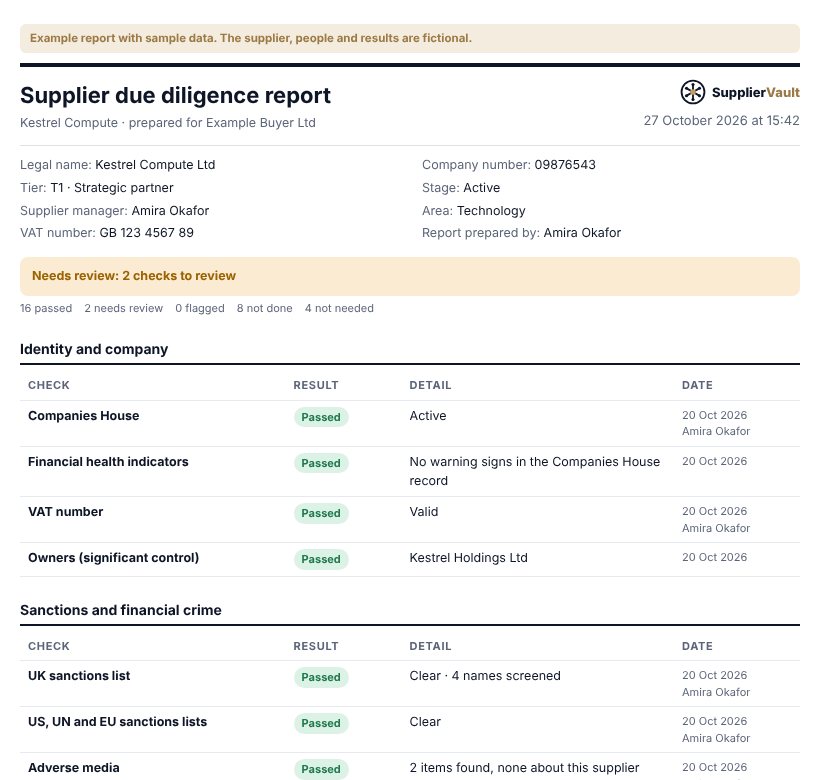
Every check for a supplier in one place: passed, needs review, flagged, not done or not needed, with the date and who recorded each result, open actions and the evidence log. Download it as a PDF with your own logo and brand colour.
Example with sample data.
Which plan includes it
| Plan | Third-party risk |
|---|---|
| Every plan | Tier assessment and tier-based onboarding checklists, security questionnaire, privacy assessment, code of conduct with forced labour and anti-bribery declarations, country risk ratings, sanctions results recorded by hand, bank detail fraud checks, named go-live sign-off and the audit trail. |
| Professional and Enterprise | The Third-party risk module: the assessment request, inherent and residual risk, scheduled re-assessments and the TPRM register. Plus automatic UK, US, UN and EU sanctions screening, Companies House owners and monitoring, the Modern Slavery registry check, the AI adverse media search, the supplier portal and the compliance packs. |
Your free month includes everything. SupplierVault records your checks and evidence; it doesn't give legal or regulatory advice.