Everything we check, and how
All 70 checks SupplierVault runs or records, who does each one, when it happens and which plan includes it. 25 of them run automatically from official data or the rules you set.
For third-party risk managers
Tiering that sets the checks, inherent risk worked out for you, residual risk by area, re-assessments on a schedule, UK, US, UN and EU sanctions screening, owners from Companies House, an AI news search, a live risk register and evidence for every result.
Risk rating · Security and data · Sanctions · Resilience · How third-party risk works
For supply chain due diligence managers
Forced, child and prison labour questions that look past the supplier to its own supply chain, country and goods risk from public sources, how far the chain has been mapped, the supplier's own audits, warning signs, an AI news search and a signed declaration from every supplier.
Forced and prison labour · Country and goods risk · Sanctions and ownership · Sector packs · Our forced labour guide · Limits
Use only the checks you need
Nothing here is forced on you. Hide any question, choose which are required, reword them or add your own questions, sections and forms. Decide which tiers and areas each form applies to, which intake answers trigger it, and whether it blocks go-live. Compliance packs stay off until you switch them on.
Who the supplier is
Confirm the supplier is a real, active organisation, that the details you hold are right and that nobody involved has a conflict.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Intake request | Legal name as on Companies House, trading name, country of incorporation, registration number, website, what's being bought, spend, contract type and a business sponsor at Director level or above. | Your team | Before onboarding starts | Every plan |
| Companies House look-up | Company status, registered office, date of incorporation, last accounts, officers and warning signs such as overdue filings or insolvency history. The directors and owners are added to sanctions screening. | Automatic | Onboarding | Professional record by hand on every plan |
| Companies House monitoring | Changes in status (for example to liquidation), overdue accounts or confirmation statement, new insolvency history, a change of name or registered office, officers appointed or leaving, and owners added or removed. Each change creates a task for the supplier manager. | Automatic | Every week for live suppliers | Professional |
| VAT number | The supplier's VAT number is valid, using HMRC's checker on GOV.UK. | Your team | Onboarding | Every plan |
| Conflicts of interest | The requester declares any conflict, and the supplier declares any close personal or financial relationship with your staff when it signs the code of conduct. | Your teamSupplier answers | Onboarding | Every plan |
Sanctions and financial crime
Screen the supplier and the people behind it, and ask about bribery, fraud and tax evasion controls. A possible match is never treated as a finding: it goes to Legal to decide.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| UK Sanctions List screening | The supplier's legal name and up to 10 directors and owners, against the official UK Sanctions List published by the FCDO (never more than 12 hours old). A possible match opens a Legal review task due the next day. Every result is saved as evidence. | Automatic | Onboarding | Professional record by hand on every plan |
| Monthly sanctions re-screen | Every live supplier and its listed people are screened again. Names you've already reviewed and cleared aren't raised again. | Automatic | Every month | Professional |
| US, UN and EU sanctions screening New | The supplier, its directors and its owners screened against the US OFAC SDN list, the UN Security Council consolidated list and the EU consolidated financial sanctions list, each refreshed at least every 12 hours. Possible matches go to Legal; results are saved as evidence. Switch it on in Settings if you trade with the US or EU, or pay in dollars or euros. | Automatic | Onboarding, then monthly | Professional record by hand on every plan |
| Beneficial owners New | Owners (people with significant control) are read from Companies House with how they control the company, added to sanctions screening and re-screened monthly. A new or departing owner creates a task. Suppliers outside the UK name anyone who owns or controls 25% or more. | AutomaticSupplier answers | Onboarding, then weekly | Professional |
| Sanctioned ownership or control New | The supplier declares whether it, its directors or its owners are on the UK, US, EU or UN lists, or are owned or controlled (50% or more) by anyone who is. | Supplier answers | Onboarding | Professional |
| Adverse media (AI news search) New | With one click, AI searches the web for news about the supplier and its directors and owners: fraud, fines, sanctions, legal action, forced labour, safety, data breaches or insolvency. Each item comes with its source and date, and your team marks it relevant or not this supplier. Relevant items become risk tasks, and every decision is saved as evidence. | AutomaticYour team | On demand, and at re-assessment | Professional |
| Politically exposed persons | Whether any directors or owners are politically exposed persons. | Supplier answers | Onboarding | Professional |
| Bribery, fraud and tax evasion | Bribery Act 2010, the failure to prevent fraud offence and the Criminal Finances Act 2017: anti-bribery policy, training, fraud procedures, tax evasion policy, whistleblowing, and investigations in the last 5 years. Approved by Legal. | Supplier answers | Onboarding | Professional |
| Anti-bribery declaration | The supplier confirms it has procedures to prevent bribery when it signs the code of conduct. Blocks go-live. | Supplier answers | Onboarding | Every plan |
Modern slavery, forced labour and prison labour
Look past the supplier to its own supply chain. The questions separate involuntary or state-imposed prison labour, which is forced labour, from voluntary paid schemes such as the UK's release on temporary licence, which should be declared but aren't forced labour.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Modern slavery statement | Searches the government's Modern Slavery statement registry by company number and name, and saves up to 5 matching statements with links. Organisations with turnover of £36m or more must publish a statement each year. | Automatic | Onboarding | Professional record by hand on every plan |
| Forced labour declaration New | The supplier confirms it doesn't use forced, bonded or child labour or involuntary prison labour, and requires the same of its own suppliers. Part of the code of conduct, so every supplier signs it before go-live. | Supplier answers | Onboarding | Every plan |
| Prison and detainee labour New | Whether prison or detainee labour is used to make the goods or deliver the services, by the supplier or anyone in its supply chain: no, only through a voluntary paid scheme, other prison labour, or don't know. Anything other than no needs details of the country, scheme, pay and how it was checked. Goods made in foreign prisons can't be imported into the UK. | Supplier answers | Onboarding | Professional |
| State-imposed forced labour New | Whether goods, materials or components could come from a region or programme where a government imposes forced labour, the term the ILO and UK Parliament use. | Supplier answers | Onboarding | Professional |
| Forced labour warning signs New | Recruitment fees charged to workers and identity documents held by employers or agents, two of the ILO's indicators of forced labour. Plus any forced or child labour found in the last 3 years and what was done. | Supplier answers | Onboarding | Professional |
| Policy and flow-down New | A policy banning forced, bonded, child and involuntary prison labour that applies to the supplier's own suppliers, and whether its contracts require the same. | Supplier answers | Onboarding | Professional |
| Supply chain mapping New | How far the supplier has mapped the supply chain for what it supplies to you: direct suppliers only, their main suppliers, back to raw materials, or not mapped. Plus the countries its main suppliers operate in. | Supplier answers | Onboarding | Professional |
| Supplier's own audits | Whether the supplier audits its own suppliers for forced or child labour, how (self-assessment, independent audit such as SMETA, SA8000 or RBA, or certification) and when it last did. | Supplier answers | Onboarding | Professional |
| Grievance and remedy New | Whether workers in the supply chain can raise concerns confidentially, and whether there's a process to put things right if forced labour is found. | Supplier answers | Onboarding | Professional |
| Labour standards on site and in agencies | Right to work checks, National Living Wage, agency workers rules, umbrella companies and pension auto-enrolment, through the Facilities and People and HR packs. | Supplier answers | Onboarding | Professional |
Financial health
Spot a supplier that might fail, or one that depends too heavily on you.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Financial health indicators | Read from Companies House: Concern (insolvency case, or not active), Watch (overdue accounts or confirmation statement, 3 or more outstanding charges, or dormant accounts while supplying you) or OK. Not a credit score. | Automatic | Onboarding, then weekly | Professional |
| Financial viability check | A Finance task for every T3 supplier and above. | Your team | Onboarding | Every plan |
| Financial stability review | Latest accounts reviewed, turnover, and your spend as a share of their turnover. Above 25% means they may depend on you. | Your team | Onboarding for T1 and T2 | Professional |
Information security and data protection
The checks your information security and data protection teams expect, triggered by what the supplier will touch rather than asked of everyone.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Third-party risk assessment request | The business owner records access to internal systems, confidential information, critical operations, intellectual property or source code, and software development, plus the service and cloud type. Approved by Security. Required when the supplier has system access, handles personal data or is critical. | Your team | Onboarding | Professional |
| Security questionnaire | SOC 2 Type II, ISO 27001, multi-factor authentication, encryption at rest and in transit, a penetration test in the last 12 months, Cyber Essentials level and expiry, how fast incidents are reported, and sub-processors. Approved by Security. | Supplier answers | Onboarding, refreshed at re-assessment | Every plan |
| Incidents and breaches New | Security incidents or personal data breaches affecting customers in the last 3 years, and what the supplier changed. | Supplier answers | Onboarding, refreshed at re-assessment | Every plan |
| Cyber insurance New | The supplier's cyber insurance cover. | Supplier answers | Onboarding | Every plan |
| Internal privacy assessment | Whether personal data is processed, data categories and subjects, where it's processed and hosted, the international transfer mechanism, the sub-processor list, a DPIA and any conditions. Approved by your privacy team. | Your team | Onboarding, refreshed at re-assessment | Every plan |
| Contract terms and DPA | A task to agree terms and the data processing agreement, for every T3 supplier and above. | Your team | Onboarding | Every plan |
| Technology and software pack | Certificates with dates, last pen test, where data is stored and accessed from, sub-processors, uptime and service credits, support hours, getting your data back at exit, source code escrow and WCAG 2.2 AA accessibility. | Supplier answers | Onboarding | Professional |
| Trust centres | Larger suppliers can point to their own trust centre or document portal instead of answering a section. Your team gets a task to check what's there. | Supplier answersYour team | Onboarding | Professional |
| ISO 27001 supplier controls | A checklist mapped to ISO 27001 controls A.5.19 to A.5.23, including sub-suppliers known and requirements flowed down, and residual risk accepted by a named manager. | Your team | Ongoing | Every plan |
Third-party risk rating
Every supplier gets a tier and a risk rating, and higher tiers and higher risk mean more checks, more often. See how third-party risk works.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Tier assessment | Five questions (criticality, data sensitivity, regulatory exposure, alternatives and integration) plus annual value recommend a tier from T1 Strategic to T4 Transactional, with the reasons. | Your teamAutomatic | Onboarding, and when things change | Every plan |
| Inherent risk | Worked out for you from the tier, the data the supplier holds, access to your systems or sites, and its use of AI with your data. | Automatic | Always up to date | Professional |
| Residual risk | Rated Low, Medium or High across security, financial, data protection and geographic or concentration risk. The worst rating sets the overall residual risk. | Your team | Each assessment | Professional |
| Scheduled re-assessments | T1 every 3 months, T2 every 6, T3 every 12 and T4 when something changes. High inherent risk means at least every 6 months. Each re-assessment creates tasks for Legal, Security, Finance, Privacy and Procurement. | AutomaticYour team | By tier | Professional |
Country and goods risk
Where a supplier is based and where its goods come from can matter as much as who it is. SupplierVault rates each country from free public sources, and shows which goods from that country are on the US Department of Labor's list of goods produced with forced or child labour.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Country risk rating New | High, Medium or Low for the country a supplier is based in and each country its goods or services come from, with the reasons: corruption score, FATF black or grey list, UK sanctions regimes and goods reported to be made with forced or child labour. The highest rating is shown against the supplier to inform its geographic risk. | AutomaticYour team | Onboarding and re-assessment | Every plan |
| Goods made with forced or child labour New | For each country, the goods on the US Department of Labor's list, marked forced labour, child labour or both, so you can see whether what you buy is on it. | Automatic | Onboarding and re-assessment | Every plan |
| Sources and dates New | Transparency International Corruption Perceptions Index 2025; FATF lists of 19 June 2026; US Department of Labor List of Goods Produced by Child Labor or Forced Labor, 2024 edition; GOV.UK current UK sanctions regimes. Each source is named on the supplier record. | Automatic | Refreshed when a source publishes a new edition | Every plan |
Bank details and payment fraud
Change-of-bank-details fraud is one of the most common frauds UK organisations face. These checks are on every plan.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| New supplier bank details | A penny test and a call-back on a number you already hold. Invoices are held until both are recorded. Only the last 4 digits of an account are ever stored. | Your team | Onboarding | Every plan |
| Change of bank details | Invoices go on hold the moment a change is logged. Your team records warning signs, calls back on a known number, checks Confirmation of Payee and runs a penny test. A second person, never the one who made the call-back, releases payments. The system enforces this. | AutomaticYour team | Whenever a change is requested | Every plan |
| Orders to unverified suppliers | Purchase requests can't go ahead until the supplier's bank details are verified and its contract is in date. | Automatic | Every purchase request | Every plan |
Operational resilience and concentration
What happens to your service if the supplier stops, and whether you rely on one supplier, or one hidden provider, for too much.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Business continuity and recovery New | Whether the supplier has a business continuity and disaster recovery plan tested in the last 12 months, and how quickly the service would be back after a major outage. | Supplier answers | Onboarding | Every plan |
| Fourth parties New | The hosting providers, data centres and key subcontractors the service depends on, so you can spot several suppliers relying on the same provider. | Supplier answers | Onboarding | Every plan |
| Business-critical flag | If the intake says the service is business-critical, the third-party risk request becomes required and the recommended tier goes up. | Automatic | Intake | Every plan |
| Service levels and owners | SLAs and service credits defined, and named commercial and technical owners on both sides, for T2 and T1 suppliers. | Your team | Onboarding | Every plan |
| Exit, continuity and concentration | An exit and continuity plan, a concentration-risk review and an executive sponsor for every T1 supplier. On Professional, concentration and continuity are reviewed again at each re-assessment. | Your team | Onboarding | Every plan |
| Material outsourcing (FCA-regulated firms) | Whether the arrangement is material or critical, the exit plan and when it was last tested, audit and access rights, sub-outsourcing consent and concentration risk. | Your team | Onboarding for T1 and T2 | Professional |
Insurance, certificates and sector checks
Ready-made compliance packs ask the questions UK law and good practice expect for what you buy. Every date that's a certificate is tracked to its expiry.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Certificates tracked to expiry | Insurance (public, employer's and professional indemnity), health and safety accreditation, Gas Safe, SIA, waste carrier, controls reports, Cyber Essentials, ISO 27001, SOC 2 and export-control classification. Expired and expiring certificates are listed on the Documents page and, on Professional, flagged in the TPRM register. On Professional, suppliers upload proof through the portal. | AutomaticYour team | Ongoing | Every plan |
| Facilities and on-site contractors | Insurance, health and safety policy and accreditation, RAMS, reportable accidents, COSHH, asbestos, CDM 2015, permits to work, trade registrations, food hygiene and allergens, right to work, DBS, TUPE and energy broker fees. | Supplier answers | Onboarding | Professional |
| People and HR suppliers | Employment agency conduct rules, agency workers' equal treatment, right to work, pension auto-enrolment, umbrella companies and the April 2026 rules, IR35 status determinations, and payroll controls. | Supplier answersYour team | Onboarding | Professional |
| Professional and advisory services | Regulator and number, professional indemnity cover and expiry, conflicts, auditor independence, named people, IR35 and anti-money-laundering ID. | Supplier answers | Onboarding | Professional |
| Marketing, agencies and media | Who owns the work, third-party rights, advertising codes, influencer labelling, marketing consent under UK GDPR and PECR, generative AI, and media rebates. | Supplier answers | Onboarding | Professional |
| Carbon reduction and ESG | Net-zero year, carbon reduction plan, Scope 1 and 2 reporting and ISO 14001. | Supplier answers | Onboarding | Professional |
AI use
Know which suppliers use AI with your data, and approve it before they go live.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| AI use assessment | What AI does in the service, which models or providers, whether your data trains AI, where it's processed, decisions about people and the human check, notice before new AI features or sub-processors, and ISO/IEC 42001 certification. Blocks go-live when the intake says AI is used. | Supplier answers | Onboarding | Professional |
| AI governance review | Your AI governance team approves the use, records the EU AI Act category where it applies, and sets conditions. Terms are re-checked at least every 12 months. | Your team | Onboarding, then yearly | Professional |
| ISO/IEC 42001 module | An optional AI register, risk and impact assessments, policy, Statement of Applicability, audits and an evidence pack. | Your team | When you switch it on | Professional |
Contracts, performance and exit
Due diligence doesn't stop at go-live. These keep the record true for the life of the contract and close it cleanly.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Notice and renewal deadlines | Notice and change-figures deadlines worked out from the contract, with warnings before an auto-renewal. Termination rights and the liability cap are recorded. | Automatic | Ongoing | Every plan |
| Obligations and milestones | Promises in the contract, such as monthly reports, right to audit, insurance certificates and service credits, each with an owner and due date. | Your team | Ongoing | Every plan |
| Reviews and surveys | Scorecards, stakeholder questionnaires, QBR packs and feedback from the supplier on working with you. Low scores become improvement actions. | Your teamSupplier answers | By tier | Professional |
| Offboarding | Notice served, access revoked and hardware recovered, data returned with a deletion certificate, DPA terminated, final account settled and bank details removed. | Your teamSupplier answers | At exit | Every plan |
Controls on your own team
Auditors look at how decisions were made, not just what was checked.
| Check | What it covers | Who does it | When | Plan |
|---|---|---|---|---|
| Named go-live sign-off | Nobody goes live until every go-live gate is green and a named person with the authority the tier needs signs it off. Even T4 suppliers. | AutomaticYour team | Go-live | Every plan |
| Separation of duties | Optionally, a supplier's own manager can't approve it to go live, and nobody can approve on their behalf while covering. | Automatic | Go-live | Every plan |
| Approval limits | Your own spending rules for purchase requests, on top of the budget holder's sign-off. | Automatic | Every purchase request | Every plan |
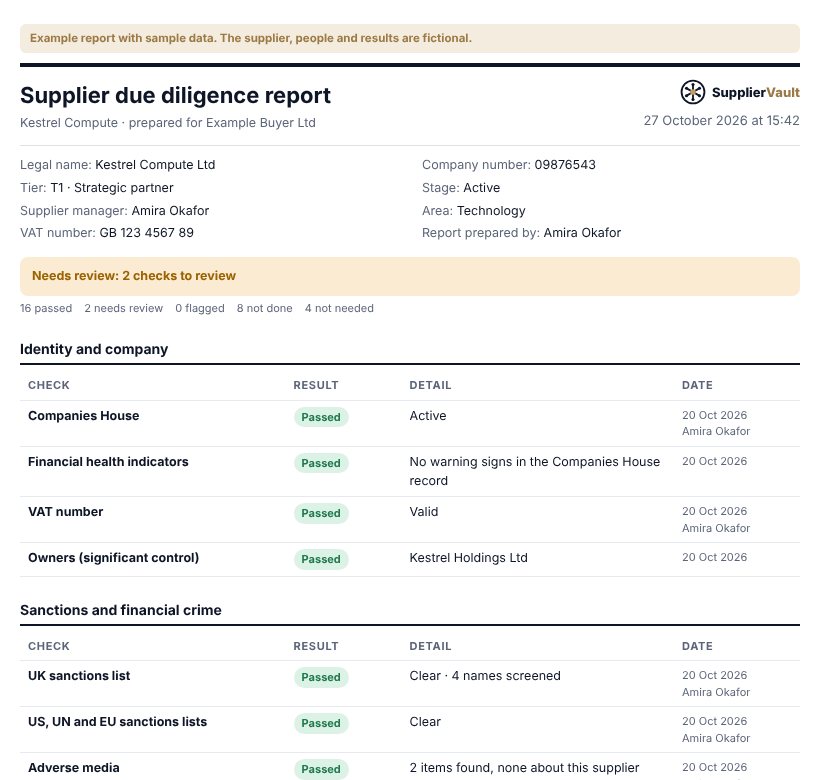
| Due diligence summary and report New | Every supplier's checks in one list, each marked Passed, Needs review, Flagged, Not done or Not needed, with the date and who recorded it. Download it as a PDF report, with open actions and the evidence log, to share with auditors or your board. | Automatic | Any time | Every plan |
| Tamper-evident audit trail | Every change is recorded with the person and the time, and chained so edits would show. Evidence can be added but never deleted. | Automatic | Always | Every plan |
One report for auditors, boards and customers
Every check for a supplier in one place: passed, needs review, flagged, not done or not needed, with the date and who recorded each result, open actions and the evidence log. Download it as a PDF with your own logo and brand colour.
Example with sample data.
What SupplierVault doesn't do
So you know where you'll still need another source.
- Other countries' sanctions lists. SupplierVault screens the UK, US OFAC, UN and EU lists. It doesn't screen other lists, such as Switzerland, Canada or Australia.
- Credit scores. Financial health indicators come from Companies House filings, which can be months old. They aren't a credit score or a credit limit.
- Ownership of non-UK companies. Owners are read automatically only for companies on the UK Companies House register. For others, SupplierVault records what the supplier declares.
- Country risk scores from paid providers. Country ratings come from free public sources, listed with their dates. They're a guide for your own assessment, not a finding about the supplier.
- Mapping or tracing your suppliers' own suppliers. SupplierVault asks each supplier how far it has mapped its supply chain and records what it tells you. It doesn't trace goods to their origin or check import records.
- Audits on site. SupplierVault records your audits and the supplier's own audit evidence. It doesn't carry out audits.
- Legal advice. Packs and questions are guides to what to ask. Check with your legal or compliance team that they cover your obligations.
Every question in every form and pack can be hidden, made optional or reworded, and you can add your own. Checks marked Professional are included in the Professional and Enterprise plans and in your free month. On Essentials, results can still be recorded by hand where shown. Compare plans.